Digital Fragility and the Crisis of Confidence: Assessing the Wave of National Network Outages

The recent succession of high-profile technical failures across critical U.S. infrastructure has ignited a firestorm of national anxiety, pitting official government narratives of routine maintenance against a growing public perception of systemic vulnerability. While the Trump administration maintains that the recent surge in network outages is the result of disparate technical glitches and poorly executed infrastructure upgrades, deep-seated skepticism persists within the federal bureaucracy and among the American public. As air traffic, financial institutions, and secure government channels stumble simultaneously, the fragility of a hyper-connected nation has come into sharp relief.
A Chronology of Systemic Instability
The current climate of apprehension did not emerge in a vacuum. It follows what cybersecurity analysts have termed "Black October," a month-long spree of international cyberattacks that targeted hundreds of institutions globally. The cumulative effect of these incidents, compounded by the Nvidia corporate espionage scandal, set the stage for a period of heightened sensitivity regarding national digital security.
The timeline of the most recent disruptions highlights the rapid succession of events that have unsettled the American populace:
- Mid-November: The Pentagon officially launched the "FORTRESS" initiative, a strategic program mandating that major U.S. military installations develop the capacity to operate fully off-grid for up to 90 days. The move signaled a formal acknowledgment by the Department of Defense that supply chain and power grid security are now top-tier national security priorities.
- Thursday, Nov 12: Microsoft experienced a widespread outage affecting Outlook and other core productivity tools, disrupting communication for millions of corporate and government users.
- Friday, Nov 13: The Federal Aviation Administration (FAA) issued a nationwide ground stop for all commercial flights lasting over four hours. The agency later attributed the catastrophe to a copper-to-fiber cable upgrade process gone awry, though the explanation did little to quell public suspicion.
- Mid-week, Nov 18: A wave of service disruptions struck major financial and retail entities, including Chase, Wells Fargo, United Airlines, and Apple. Crucially, the National Security Agency (NSA) experienced a localized failure of its internal classified communications network, a development that intelligence insiders describe as deeply concerning.
- Friday, Nov 20: CNN reported that the FBI is currently investigating a breach of its national criminal information database, the second such incident in recent months, casting further doubt on the administration’s "maintenance-only" explanation.
The Disconnect Between Policy and Reality
The official government stance remains one of technical coincidence. Director of National Intelligence Jay Clayton, testifying before the House Homeland Security Committee, maintained a firm line: "These are separate service outages associated with maintenance and technical changes. They are not a coordinated or state-sponsored attack."
However, this rhetoric has struggled to gain traction even within the agencies responsible for emergency response. Two officials at the Federal Emergency Management Agency (FEMA), speaking on the condition of anonymity, expressed profound doubts to the Washington Post. "There is nothing on this scale that has happened before in this many sectors this close together," one official stated. "This is scary, and there is no leadership."
The internal tension is further underscored by the White House’s sudden dismissal of National Cyber Director Sean Cairncross on the Thursday following the initial wave of outages. While the administration has not explicitly linked his removal to the technical failures, the timing has been interpreted by many policy analysts as a signal of internal dissatisfaction with the current state of federal cybersecurity posture.
Economic and Societal Repercussions
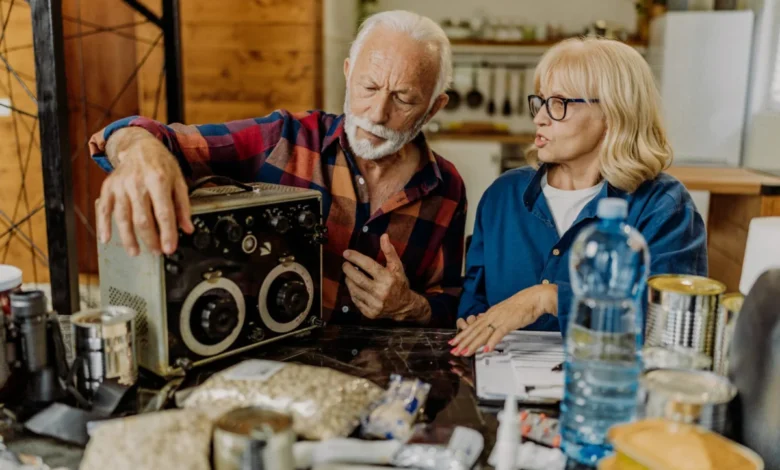
The psychological impact of these outages has manifested in tangible shifts in consumer behavior. Across the country, retail giants like Costco and Walmart have reported a significant uptick in the sale of emergency provisions, including shelf-stable food, water, and portable power solutions.
"Consumer anxiety, following the Microsoft Outlook outage, the ground stoppage for all U.S. airline flights, and apocalyptic concerns flaring up across social media, have all contributed to increased emergency prep sales," noted Mizuho analyst David Bellinger. This trend is mirrored internationally, with the United Kingdom government recently issuing guidance for its citizens to maintain a three-day supply of cash, water, and non-perishable food—a move that has echoed throughout the American consciousness.
The financial sector, already skittish, has seen significant market volatility. Equity markets have experienced some of their sharpest declines since the onset of the pandemic, driven by fears that the end of the AI-led productivity boom, coupled with infrastructure instability, could trigger a broader economic downturn. Investors are increasingly concerned that the very systems powering modern commerce are fundamentally brittle.
Expert Analysis: Is it Coincidence or Coordinated?
Despite the public panic, experts in network architecture urge a more measured interpretation. Mark Giles, director of Ookla Research—the parent company of Downdetector—argues that while the volume of outages is unprecedented, the technical nature of each event remains distinct.
"This is a big blip, but it’s kind of on par for the course for what we’re seeing in terms of those longer-term trends," Giles explained in an interview. "Most of the time they’re fairly self-contained and remedied quite quickly. It’s the ones where you can’t withdraw money or you can’t access your emails that really get the headlines."
Giles suggests that the rush to patch vulnerabilities discovered during "Black October" may be the culprit. The rapid deployment of software updates and hardware upgrades across aging infrastructure—undertaken precisely to avoid future attacks—may have introduced the very instability that is currently causing the outages. In this view, the "cure" is creating a temporary period of heightened volatility as systems adjust to new protocols.
The Broader Implications for National Security
Regardless of whether the outages are the result of malicious activity or administrative oversight, the broader implications remain the same: the United States is currently experiencing a crisis of confidence in its critical infrastructure.
The perspective of citizens, such as 68-year-old Chuck Amasio, reflects a new reality in how Americans perceive modern conflict. "We talk about how wars aren’t done with bombs anymore," Amasio observed while stranded at Newark Liberty International Airport. "They shut down airspace or a power grid. They can cripple an economy."
This shift in public mindset poses a unique challenge to the administration. Even if the government’s technical assessment—that these are non-malicious, maintenance-driven outages—is entirely accurate, the failure to effectively communicate this to a skeptical public is driving a surge in isolationist behavior and economic anxiety.
Moving forward, the federal government faces a two-fold challenge. First, it must accelerate the modernization of legacy infrastructure to prevent the vulnerabilities that necessitated these emergency patches. Second, it must re-establish transparency. As long as internal dissent continues within agencies like FEMA and the FBI continues to report potential breaches, the narrative that these events are "routine" will continue to lose ground to the fear that the nation’s digital spine is failing under the weight of its own complexity.
For now, the country remains in a state of watchful waiting. Whether the recent string of failures represents the "new normal" of a digitized society or a temporary growing pain of a massive technological upgrade cycle remains to be seen. What is clear is that the threshold for public trust in digital infrastructure has been permanently lowered, and the path to restoring that trust will require more than just assertions of technical innocence; it will require a transparent, robust, and unified strategy for national resilience.